Skip to content

IT security for biotech and life sciences

How well is your research data protected?
In three days you will know.

For the management of research-driven biotech and life science companies, from start-up to scale-up. We review your entire IT, from the analysis pipelines and raw data in the cloud and the access your research partners have to the computers next to your lab instruments, together with your IT or your IT provider. Then we close the gaps and, if you wish, look after security on an ongoing basis. We only make changes with your approval.

Bastian Wenske

Founder and managing director

Book an introductory call
How it works 
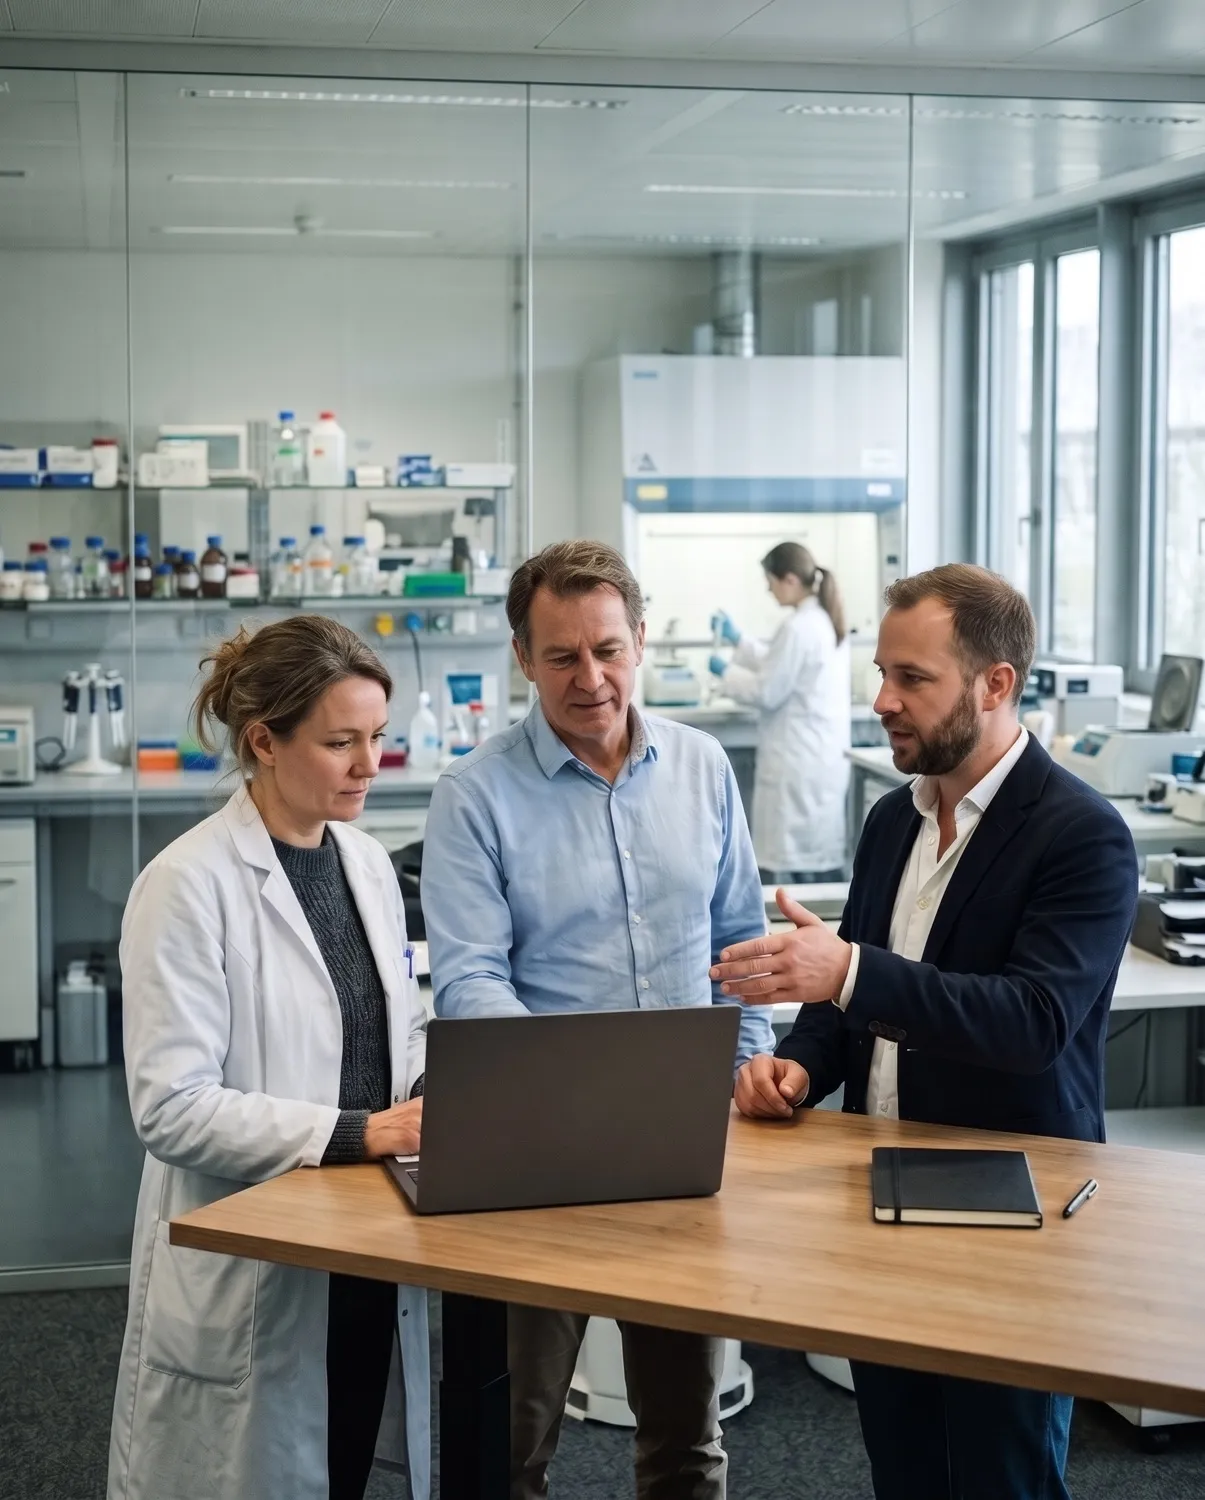
A scientist in a lab coat and the managing director look at a laptop with a consultant, behind the glass wall a colleague works in the lab
For whom
Research-driven biotech and life science companies, spin-offs from research institutes, from start-up to scale-up
First step
IT security check on site, three days, we change nothing
In scope
Research data and cloud storage, analysis pipelines, accounts and guest access, admin rights, lab computers, backups
Then
Implement, ongoing care, or a documented handover to your IT
Price
Fixed price for the IT security check, quote after the introductory call

Projects for organisations including

Sound familiar?

Typical situations in research-driven companies

The value of your company lies in data: sequences, screening results, models, lab notebooks. IT is often looked after by a small team or a provider, sometimes by a colleague alongside their research. We review what runs at your company. You do not need technical knowledge for the call.

The raw data sits in the cloud

Analysis pipelines run in the cloud, and the storage holding raw and result data grows with every project. Some of it is shared more widely than intended, access keys sit in scripts, and nobody knows exactly who has which rights.

Research partners keep their guest access

Every joint project adds guest accounts, shared folders and another tool. When the collaboration ends, the access often stays.

Scientists are admins on their own computers

Anyone who has to install analysis tools themselves gets admin rights. In day-to-day research that is understandable. It also lets an attacker move on easily from the first compromised computer.

An old Windows version runs next to the lab instrument

The vendor only supports the instrument software on that version, so the computer next to it stays as it is. Whether it can be reached from the rest of the network, nobody has checked for a long time.
A common occasion

Partners and investors want to know

Anyone who shares data or licences with you, or invests in you, asks how you protect your intellectual property. After the check you can answer in writing.

A pharma partner sends a security questionnaire

Before a collaboration or licence, the partner wants to know how you protect data, access and backups, often with evidence. You should only sign what is true.

Customer security questionnaires

Investors ask during due diligence

In a financing round or a sale, the review can include IT security. A current report with a plan of measures shows that you know where you stand and are working on it.

About the IT security check

Bastian Wenske

Founder and managing director

Discuss your situation

How does the collaboration work?

You start with a manageable fixed-price step and decide afterwards how to continue. The lab and your analyses keep running during the check.

  1. 30 minutes

    Introductory call

    You speak directly with Bastian Wenske, founder and managing director. We clarify what runs at your company, who looks after it and what the check should cover.

  2. 3 days, fixed price

    IT security check

    On site we review network, servers, workstations and lab computers, cloud accounts and data storage, guest access and backups. We change nothing.

  3. Based on findings

    Secure

    Close the largest gaps first, done by your IT, your IT provider or us.

  4. Your choice

    Ongoing care or handover

    We look after security on an ongoing basis, or your IT takes it over with documentation.

How well is your research data protected today?

The IT security check shows in writing where your company is exposed and what to do first. With the report you can also answer the questions of partners and investors. At a fixed price.

Bastian Wenske

Founder and managing director

Book an introductory call
Request the IT security check 

Two paths

Ongoing care or taking over yourself

Both paths lead to the same standard. After the check you decide which one suits your company.

We look after security for you

At a fixed monthly price we review security alerts, respond to incidents and report to you every month on what has happened. Access, data and documentation stay with you.

Managed Security

We hand over to your IT with documentation

We implement the measures and hand them over to your IT team or your IT provider with documentation and written instructions.

About the IT security check

Frequently asked questions

How does a biotech company protect its research data?

With a few basics that are applied consistently. You know where the data is and who can access it. Every account, including those of partners, signs in with a second factor. Admin rights run through separate accounts. And an attacker cannot delete the backups along with everything else, and restoring them has been tested. The check shows which of these are in place at your company and what is missing.

A pharma partner has sent us a security questionnaire. What do we do?

First establish which answers are true today, then close the gaps in a targeted way. After the check you have this in writing. Many questions can then be answered with reference to the report, and for open points you give a date by which they will be done.

How do we prepare for IT questions in due diligence?

Which questions come up depends on the investor. Typical ones are: where is the research data, who has access, is there a tested backup, and what happens in an incident? With a current report and a plan of measures you can show this instead of only asserting it.

Our lab instruments run on old Windows. Do they need replacing?

Usually not. It is often enough to separate these computers from the rest of the network and route the vendor’s remote access through a controlled access point. We do not change the instruments or their software. The check shows which devices are affected and what makes sense in each case.

Do our scientists have to give up their admin rights?

Not without a replacement. Anyone who needs to install tools can keep doing so, for example with a separate admin account or a time-limited approval. We agree with your teams how to do this with the least disruption to research.

Will the check disrupt running experiments or analyses?

No. We look at the systems and read out settings without changing anything. We do not touch lab instruments or running pipelines, and we agree times in the lab with your lab management.

Who gets to see our research data?

Only the people at WCS who work on your project, and only as far as the work requires. We sign a non-disclosure agreement with every customer, and our employees present a certificate of good conduct before they are hired. Where a project requires it, we assign consultants with a government security clearance.

What does the IT security check cost?

The check has a fixed price that depends on the size of your IT. You receive the written quote after the introductory call, before the check begins. What follows is your decision, with the report in hand.

Let's talk about your IT security

In the introductory call (30 minutes, no obligation) we clarify:

  • where your company stands today and what concerns you most
  • which next step makes sense for your organisation
  • what effort and price range to expect
Bastian Wenske

Bastian Wenske

Founder & Managing Director

Heidelberger Straße 15
12059 Berlin
Germany

Prefer to reach out directly? Send us an email at [email protected].