Attack paths in Entra ID: how a single phishing click becomes a tenant takeover
Key takeaways
- A tenant takeover is rarely a single mistake. It is a chain: stolen session, mailbox, internal phishing or app consent, privileged role, persistent access.
- Every link in that chain can be broken with built-in Microsoft Entra ID controls. Breaking it early prevents the expensive later steps.
- Phishing-resistant sign-in, Conditional Access with device conditions, Privileged Identity Management and restricted user consent are the four most effective levers.
- Without audit logs that someone actually reviews, you cannot tell whether an attacker has already set up persistence. A password reset alone does not end a compromise.
When we run a penetration test against a Microsoft 365 environment, we do not ask whether a phishing click is possible. It almost always is. We ask how far an attacker gets afterwards. For management, that is the question that matters: a compromised mailbox is an incident, while a compromised tenant affects email, files, Teams, device management and often Azure at the same time. This article walks through the typical chain from the attacker’s point of view, step by step, and names the control that breaks it at each stage.
What does a typical attack path in Entra ID look like?
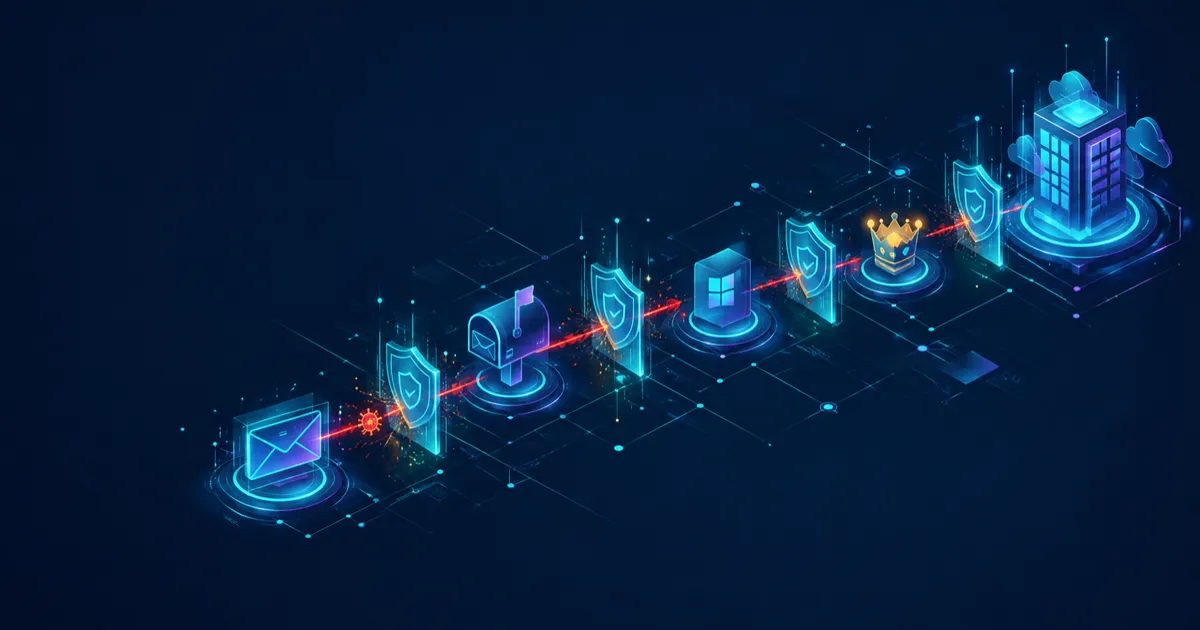
Microsoft Entra ID (formerly Azure Active Directory) is the identity service behind Microsoft 365 and Azure. Whoever controls a privileged identity there controls the environment. The chain we see again and again in tests has five links:
| Step | What the attacker gains | Control that breaks the step |
|---|---|---|
| 1. Phishing, token theft | A valid session of an employee | Phishing-resistant MFA, Conditional Access with a device condition |
| 2. Mailbox and OneDrive | Reading mail, data, contacts, invoice processes | Continuous Access Evaluation, revoking sessions, risk policies |
| 3. Internal phishing, app consent | More accounts, an attacker-controlled app with data access | Restricted user consent, admin consent workflow |
| 4. Privileged role or app | Administrative control of the tenant | PIM, separate admin accounts, reviewing roles held by apps |
| 5. Persistence | Access that survives a password reset | Audit logs, alerting, protecting MFA registration |
Step 1: phishing and token theft
Traditional MFA with push approval or one-time codes does not stop adversary-in-the-middle phishing. A phishing page relays the real Microsoft sign-in and, once MFA has succeeded, captures the session cookie. The attacker now holds a signed-in session and never needs the password. A variant is device code phishing, where the victim enters a code on the genuine Microsoft page and thereby grants access to the attacker’s device.
What breaks it: phishing-resistant methods such as passkeys (FIDO2), Windows Hello for Business or certificate-based authentication. They bind the sign-in cryptographically to the real domain, so a proxy page gets nothing it can reuse. On top of that, Conditional Access requires a compliant or hybrid-joined device, so a stolen session from an unknown machine does not get further. If you do not need the device code flow, block it in Conditional Access under Conditions > Authentication flows.
Step 2: mailbox and OneDrive
With the session, the attacker reads email, searches files for invoices, contracts and credentials, and often creates inbox rules that hide replies. This is the point at which an IT incident can turn into payment fraud or a reportable data breach.
What breaks it: Continuous Access Evaluation (CAE) makes Exchange Online, SharePoint Online and Teams react to critical events such as disabled accounts, password changes or revoked sessions in near real time, rather than waiting for the token to expire. According to Microsoft, this critical event evaluation is available in every tenant. With Microsoft Entra ID P2 you can add risk-based policies from ID Protection that require a fresh strong sign-in or block access when a sign-in looks suspicious. One point for existing tenants: Microsoft retired the legacy risk policies configured directly in ID Protection on 1 October 2026. Risk policies now belong in Conditional Access.
Step 3: internal phishing and app consent
Sent from a real mailbox, the next phishing email is credible because it comes from a known colleague. The targets are accounts with more rights, for example in IT or finance. A second route is an application: the attacker gets a user to consent to an app, which then accesses mail or files with that user’s permissions. This access does not depend on the password and survives a reset.
What breaks it: new tenants now use the Microsoft-managed consent setting, under which users can no longer grant mail and file permissions themselves. Older tenants often still let users consent to apps for every permission that does not require admin consent. Microsoft recommends restricting this: user consent only for apps from verified publishers and only for permissions classified as low impact, with everything else going through the admin consent workflow. You find the setting in the Entra admin center under Enterprise apps > Consent and permissions > User consent settings.
Step 4: privileged role or app
The goal is a role such as Global Administrator, Privileged Role Administrator or Application Administrator. The last one is often underestimated: it can add credentials to applications and thereby act as an app that itself holds broad permissions. Shortcuts we frequently find in tests are permanently assigned admin roles on accounts that are also used for email, and service accounts with an admin role but no MFA.
What breaks it: Privileged Identity Management (PIM) makes roles eligible instead of permanently active. Activation is time-limited, requires strong authentication and, if you choose, an approval. PIM requires Microsoft Entra ID P2 or Microsoft Entra ID Governance licences. Equally important are separate, cloud-only admin accounts without a mailbox, used only from a hardened admin workstation. Our article on the privileged access workstation describes the concept.
Step 5: persistence
An experienced attacker sets up persistence before being noticed. Typical techniques: an additional MFA method on the compromised account, a new secret or certificate on an existing app, a new app registration with application permissions, or an additional domain configured for federation. With a federated domain whose sign-in the attacker controls, they can impersonate users of that domain without knowing their passwords.
What breaks it: a Conditional Access policy for the user action Register security information, so new MFA methods can only be added under defined conditions, plus alerts on exactly those changes that indicate persistence.
Which events should IT monitor?
The following KQL query for Microsoft Sentinel or a Log Analytics workspace surfaces the changes that point to persistence or privilege escalation in the chain above. It assumes the Entra audit logs are sent there through a diagnostic setting.
let watched = dynamic([
  "User registered security info", "Admin registered security info",
  "Add member to role",
  "Consent to application",
  "Set domain authentication", "Set federation settings on domain"]);
AuditLogs
| where TimeGenerated > ago(30d)
| where OperationName in~ (watched)
    or OperationName startswith "Add eligible member to role in PIM completed"
    or OperationName contains "Certificates and secrets management"
| extend Initiator = coalesce(tostring(InitiatedBy.user.userPrincipalName),
                              tostring(InitiatedBy.app.displayName))
| project TimeGenerated, OperationName, Result, Initiator,
          Target = tostring(TargetResources[0].displayName)
| order by TimeGenerated desc
No single row is an attack. Employees register new MFA methods every day. It becomes suspicious when several of these events occur in quick succession on the same account, or outside your normal change processes. You can turn the query into scheduled analytics rules in Sentinel.
What should you do if an account is already compromised?
A password reset is not enough. A stolen session, an additional MFA method and a consented app are all unaffected by it. The order that has proven itself:
- Block the account and revoke all sessions (Users > Revoke sessions). With CAE this takes effect in Exchange, SharePoint and Teams within minutes.
- Review registered authentication methods and remove unknown ones.
- Review the user’s app consents and revoke unknown ones.
- Check inbox rules and forwarding.
- Trace the account’s roles and the changes it made in the audit logs.
Our article on the incident response plan describes how to define these steps in advance.
What does this mean for management and liability?
For management, the attack path is an argument for prioritisation. The controls at the start of the chain, phishing-resistant sign-in and Conditional Access, prevent most of the later steps. The controls at the end, PIM and monitoring, limit the damage when something gets through anyway. NIS2 and DORA do not require that nothing ever happens. They require that risks were known, appropriate measures are in place, and an incident can be detected and reconstructed. That is what the combination of hardening and reviewed logs delivers.
Our recommended order: first phishing-resistant methods for all administrators and Conditional Access with a device condition, then restrict user consent, then PIM, and in parallel send the audit logs to a SIEM that someone actually monitors.
Next step
A penetration test of your Microsoft 365 environment shows whether the chain breaks at one of these points in your tenant. We follow the path from the attacker’s perspective and deliver a report that management and IT can both read. For implementing the countermeasures, we support the rollout of Conditional Access and the hardening of the tenant.
Frequently asked questions
Is MFA not enough to prevent a tenant takeover?
Traditional MFA with push or one-time codes stops attacks with stolen passwords, but not the theft of an already signed-in session through a proxy phishing page. Phishing-resistant methods such as passkeys and Conditional Access with device conditions address that.
Which licence do I need for the controls described?
Conditional Access requires Microsoft Entra ID P1, which is included in Microsoft 365 Business Premium and E3, for example. Privileged Identity Management requires Microsoft Entra ID P2 or Microsoft Entra ID Governance; risk-based policies from ID Protection require Microsoft Entra ID P2. Restricting user consent and revoking sessions need no additional licence.
How can I tell whether an attacker has already set up persistence?
In the Entra audit logs: newly registered authentication methods, new secrets or certificates on apps, new consents, role assignments, and changes to domain authentication or federation. These events should be collected centrally and alerted on.
How often should such an attack path be tested?
At least once a year and after major changes, for example new applications, a change of sign-in methods or a new IT service provider. Between tests, monitoring shows whether the controls are working.

 Book an introductory call